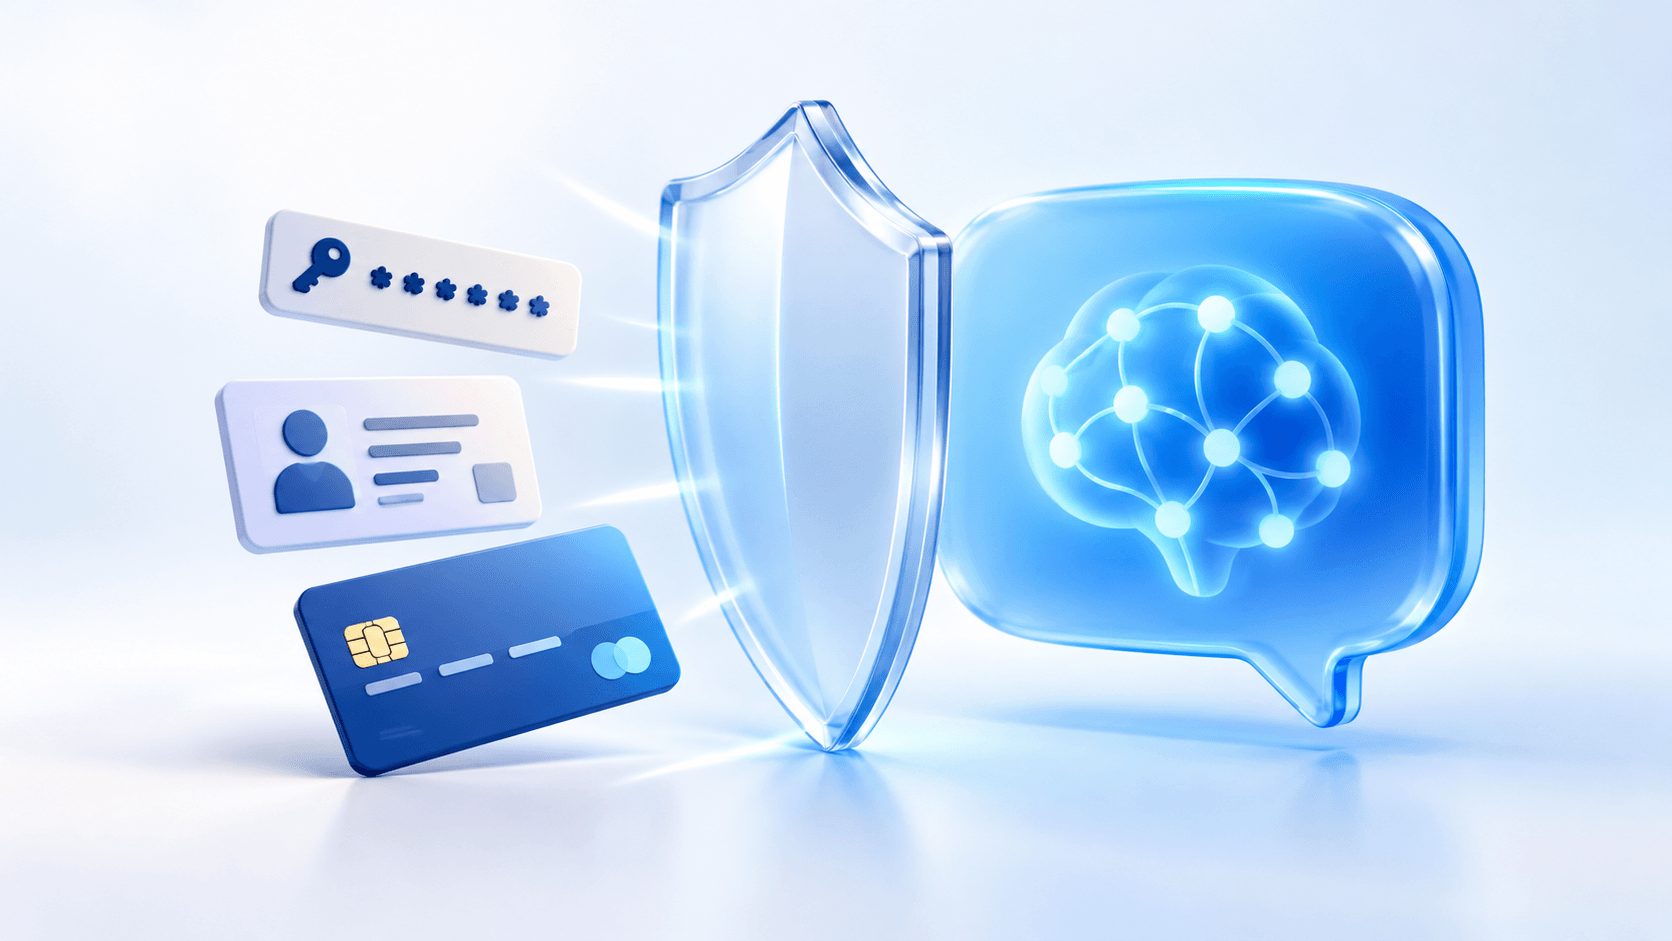
AI assistants can rewrite an email, summarize a report, review code, or turn scattered notes into a clear plan in seconds. That convenience makes it easy to forget one important fact: every prompt contains data, and some data should never leave your control.
The safest rule is simple: if you would not post the information publicly or send it to an unknown person, do not paste it into an AI tool without reviewing and removing sensitive details first. The model you choose does not change this basic responsibility.
What counts as sensitive information?
1. Passwords and access credentials
Never share passwords, one-time codes, recovery phrases, API keys, access tokens, private keys, database connection strings, or real values from a .env file. These are not harmless technical details. Any one of them may provide access to an account, server, code repository, customer database, or financial asset.
When asking for programming help, replace real secrets with obvious placeholders such as YOUR_API_KEY or EXAMPLE_DATABASE_URL. Keep the structure of the error, but remove the credential itself.
2. Financial and payment information
Do not paste full card numbers, CVV codes, bank account details, payment records, tax documents, invoices containing personal data, or customer transaction information into an AI chat.
If you need help analyzing expenses, create a small anonymized table that contains only the amount, date, and category. In most cases, names, account numbers, and transaction identifiers are not needed to complete the task.
3. Identity documents and personal identifiers
Passports, national ID cards, driver's licenses, birth certificates, signatures, Social Security numbers, addresses, phone numbers, and clear images of official documents should stay out of general AI tools.
Even a document that looks routine may contain enough information for identity theft or social engineering. Redact identifying details before asking for help with formatting, translation, or summarization.
4. Medical, legal, and highly personal records
Health reports, prescriptions, diagnoses, therapy notes, insurance records, legal files, and private family information can expose deeply personal facts. They may also be protected by privacy laws or professional obligations.
For a general explanation, describe the situation without names, dates of birth, record numbers, or unique details. For medical or legal decisions, use a qualified professional rather than relying only on an AI response.
5. Confidential business and customer data
Internal contracts, unpublished financial results, product roadmaps, employee records, customer lists, support conversations, private meeting notes, source code, security reports, and incident logs may all be confidential.
Before sharing a work document, check your organization's policy and use only approved tools. Remove company names, customer identifiers, private URLs, credentials, and any detail that could reveal a person, system, or unreleased project.
6. Other people's information
Your consent does not give you permission to share someone else's data. A colleague's email, a customer's complaint, a candidate's résumé, or a private conversation may contain information that the other person never agreed to provide to an AI service.
When possible, summarize the problem in your own words. If exact text is necessary, remove names and any detail that could identify the person.
How to use AI more safely
Share the minimum
Give the model only the information required to solve the problem. More context is not always better. A short, focused description is often both safer and more effective.
Replace real details with placeholders
Change names, companies, account numbers, domains, project names, and credentials to fictional values. Keep the relationships between the details so the example still makes sense.
Remove hidden information
Documents and images can contain metadata, comments, revision history, file paths, or text outside the visible page. Review the file carefully before uploading it.
Use approved tools for sensitive work
Business or enterprise AI services may provide stronger controls, but they are not a reason to ignore internal policy. Check how data is stored, who can access it, whether prompts are retained, and whether the service uses submitted content for model improvement.
Review before you press send
Pause for ten seconds and ask: Does this prompt contain a secret? Could it identify a person? Does it reveal confidential work? Can I explain the same problem with less data?
What should you do after sharing something sensitive?
Act quickly. Delete the conversation if the service provides that option, but do not assume deletion alone removes every risk.
If you shared a password, token, API key, or recovery code, revoke or rotate it immediately. If financial information was exposed, contact the bank or payment provider and monitor the account. For identity, medical, customer, or company data, notify the appropriate security, privacy, or legal contact and follow the incident-response process.
Write down what was shared, when it happened, and which service received it. A clear record helps the right people assess the risk and take the next steps.
A quick checklist before using an AI tool
- Have I removed passwords, tokens, and real credentials?
- Have I hidden financial and identity information?
- Have I removed names and details that identify other people?
- Does this document contain confidential company or customer data?
- Could a smaller, anonymized example solve the same problem?
- Is this tool approved for the type of information I am using?
AI can be a powerful assistant without becoming a new privacy risk. The goal is not to avoid useful tools; it is to use them deliberately. Share less, anonymize more, and treat every prompt as information you are handing to another service.